Showing posts with label Privacy. Show all posts

Thursday, March 15, 2007

Google and Privacy

Google has announced that it will be changing it's policy of data storage about you and your searches. It's a move in the right direction, though much more could be done.

"Under the new policy announced on Wednesday, which Google expects to have fully implemented by the end of the year, the company will anonymize the final eight bits of the IP address and the cookie data after somewhere between 18 months and 24 months, unless legally required to retain the data for longer."

The entire article can be found here http://news.zdnet.com/2100-1009_22-6167333.html?tag=nl.e539

Now if you are a person that likes having privacy, this could be disturbing and a lot of privacy advocates feel the same way. I'm wary of this, as information is power and could be misused, though perhaps I'm just old fashioned.

I like to think of privacy on the Internet like this, it's just like a telephone conversation, but you are using a computer, the only time your privacy should be invaded, is when you give permission for it, and there should be full disclosure in a transparent manner of what information is being stored and gathered about you. I would also like to stress it should not be in tiny Print ,but stated in a clear manner.

I would like to know your feeling's about privacy, how much should people have? Who should control that information? Who has ownership over it? Who can access it?

My opinion is that the individual should have the final say on their information and privacy. The only time that should be invaded is either when a person commits a crime or they give permission.

Wednesday, October 18, 2006

Big Brother Double Double Plus Good


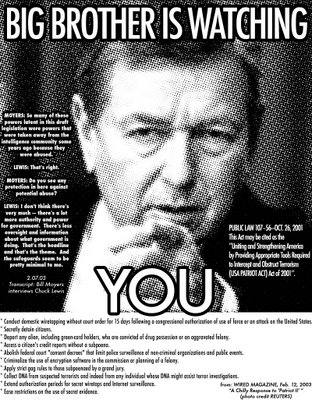
For awhile in Canada some ISP's have been keeping records on their own. I'm not really sure how I feel about this issue, as I can see the reasons for wanting to combat crime, yet I'm very worried that in the effort to do this we become what we are trying to combat and civil rights that people courageously fought for sometimes losing their life for could be compromised in this well meaning attempt.

In the end this is the question I'm struggling with I the act of fighting terrorism and cyber-crime/crime are we becoming what we are fighting against? Basically in the act of trying to prevent actions from happening do we create the circumstances in which they can thrive?

I look forward to any comments people have on this issue.

FBI director wants ISPs to track users

By Declan McCullagh

FBI Director Robert Mueller on Tuesday called on Internet service providers to record their customers' online activities, a move that anticipates a fierce debate over privacy and law enforcement in Washington next year. "Terrorists coordinate their plans cloaked in the anonymity of the Internet, as do violent sexual predators prowling chat rooms," Mueller said in a speech at the International Association of Chiefs of Police conference in Boston. ISP snooping time line

In events that were first reported by CNET News.com, Bush administration officials have said

Internet providers must keep track of what Americans are doing online.

June 2005: Justice Department officials quietly propose data retention rules.

December 2005: European Parliament votes for data retention of up to two years.

April 14, 2006: Data retention proposals surface in Colorado and the U.S. Congress.

April 20, 2006: Attorney General Alberto Gonzales says data retention "must be addressed."

April 28, 2006: Rep. Diana DeGette proposes data retention amendment.

May 16, 2006: Rep. James Sensenbrenner drafts data retention legislation--but backs away from it two days later.

May 26, 2006: Gonzales and FBI Director Robert Mueller meet with Internet and telecommunications companies.

June 27, 2006: Rep. Joe Barton, chair of a House committee, calls new child protection legislation "highest priority."
"All too often, we find that before we can catch these offenders, Internet service providers have unwittingly deleted the very records that would help us identify these offenders and protect future victims," Mueller said. "We must find a balance between the legitimate need for privacy and law enforcement's clear need for access." The speech to the law enforcement group, which approved a resolution on the topic earlier in the day, echoes other calls from Bush administration officials to force private firms to record information about customers.


Attorney General Alberto Gonzales, for instance, told Congress last month that "this is a national problem that requires federal legislation." Justice Department officials admit privately that data retention legislation is controversial enough that there wasn't time to ease it through the U.S. Congress before politicians left to campaign for re-election. Instead, the idea is expected to surface in early 2007, and one Democratic politician has already promised legislation.

Law enforcement groups claim that by the time they contact Internet service providers, customers' records may have been deleted in the routine course of business. Industry representatives, however, say that if police respond to tips promptly instead of dawdling, it would be difficult to imagine any investigation that would be imperiled. It's not clear exactly what a data retention law would require. One proposal would go beyond Internet providers and require registrars, the companies that sell domain names, to maintain records too. And during private meetings with industry officials, FBI and Justice Department representatives have cited the desirability of also forcing search engines to keep logs--a proposal that could gain additional law enforcement support after AOL showed how useful such records could be in investigations.

A representative of the International Association of Chiefs of Police said he was not able to provide a copy of the resolution. Preservation vs. retention At the moment, Internet service providers typically discard any log file that's no longer required for business reasons such as network monitoring, fraud prevention or billing disputes. Companies do, however, alter that general rule when contacted by police performing an investigation--a practice called data preservation.

A 1996 federal law called the Electronic Communication Transactional Records Act regulates data preservation. It requires Internet providers to retain any "record" in their possession for 90 days "upon the request of a governmental entity." Because Internet addresses remain a relatively scarce commodity, ISPs tend to allocate them to customers from a pool based on whether a computer is in use at the time. (Two standard techniques used are the Dynamic Host Configuration Protocol and Point-to-Point Protocol over Ethernet.)

In addition, Internet providers are required by another federal law to report child pornography sightings to the National Center for Missing and Exploited Children, which is in turn charged with forwarding that report to the appropriate police agency. When adopting its data retention rules, the European Parliament approved U.K.-backed requirements saying that communications providers in its 25 member countries--several of which had enacted their own data retention laws already--must retain customer data for a minimum of six months and a maximum of two years.

The Europe-wide requirement applies to a wide variety of "traffic" and "location" data, including: the identities of the customers' correspondents; the date, time and duration of phone calls, VoIP (voice over Internet Protocol) calls or e-mail messages; and the location of the device used for the communications. But the "content" of the communications is not supposed to be retained. The rules are expected to take effect in 2008.

CNET News.com's Anne Broache contributed to this report.

http://news.zdnet.com/2100-1009_22-6126877.html

Tuesday, October 17, 2006

Big Brother 1984 Double Plus Good


I don't know about you, but I find this a bit scary, it seems like in response to our fears we see enemies everywhere, is it just me or does it feel like Big Brother maybe just maybe might be making a comeback, and folks it's not 1984.

OTTAWA - Federal government departments are profiling some access requesters, a veteran Ottawa researcher charged Monday.

Testifying before a parliamentary committee, Ken Rubin revealed that he learned recently he has been the subject of just such a profile.

Documents Rubin obtained from the Canadian Border Services Agency revealed a memo prepared in January 2004 for then-public safety minister Anne McLellan outlining an access request that Rubin had filed for information concerning the department's Advance Passenger Information project. In the memo, which the department told Rubin was never transmitted all the way to the minister, the department outlines details of telephone calls officials had with Rubin, other access requests he had filed and the fact that he had volunteered to help Maher Arar and his wife get information about their case.

At the time, Arar was still under suspicion by the government of being a terrorist and was on a watch list along with his wife and children.
The memo was released to Rubin earlier this month under the Access to Information Act after he filed a complaint.
''This is unacceptable,'' Rubin told the committee. ''Matching up my background data and work and separate access requests should not be used to create a profile and discuss my access usage or that of other requesters. I do not consider this kind of data being prepared and shared internally or going, or potentially going, to a minister, a positive part of, or within the spirit of the Access to Information Act.''

New Democrat MP Pat Martin said he was shocked to learn that a government department had prepared a profile of an access requester.
''I think it is an absolute bombshell that they are not only asking the identity, which I think undermines the integrity of the whole system, but they are asking about confidential personal information.''

Jason Kenney, parliamentary secretary to Prime Minister Stephen Harper, said Rubin's testimony about being profiled corresponds with some of the testimony that the committee has already heard about the way the privacy of some access requesters has been treated in the past.
''This would be, I guess, the third concrete instance that we know about. There seems to be sufficient evidence to conclude that this practice of furnishing names to political staff has happened in the past. Just how widespread or how frequent, we just don't know.''

The comment came as the committee wrapped up another day of hearings into reports that the government appears to have broken the privacy law by disclosing the name of Canadian Press reporter Jim Bronskill during a telephone conference call in which public servants from several departments discussed which reporters were working on stories related to security and to pandemic preparedness.

The information was then sent to several officials in the prime minister's office who had not participated in the call, including communications director Sandra Buckler. None of those officials reported a possible violation of the privacy act.
Privacy Commissioner Jennifer Stoddart is investigating.
Kenney could not say Monday whether the government has reviewed the minutes of the weekly security conference call to ascertain whether there were other instances of the names of access requesters being discussed.